(주) 브이웨이는 2023년 11월 27일부터 30일까지 독일의 Leonardo Royal Hotel in Munich에서 열리는 Automotive Cyber Security Europe 행사에 참여합니다. 본 행사는 ISO/SAE 21434와 R155/R156의 대응을 위해 여러가지의 도전 과제들에 대한 의제를 나누고 해결점을 찾기 위해 유럽 및 전세계의 CyberSeucirty 전문가들이 모이는 컨퍼런스입니다.
특히 자사의 유럽 및 미국 영업 담당자인 Stephen Porter가 어떻게 STPA가 Cybersecurty에 활용될 수 있으며 ISO/SAE 21434에서 수행되는 TARA의 분석을 어떻게 뒷받침 할 수 있는지 발표가 준비되어 있습니다.
MAIN STAGE DAY TWO – WEDNESDAY 29th NOVEMBER 2023
12:20 PM HOW STPA IS BEING USED IN AUTOMOTIVE CYBERSECURITY
STPA represents a new paradigm that is being applied in safety analysis and management within our industry - It’s application in cybersecurity, to improve resilience against cyber disruptions through STPA-Sec is new to many. In this presentation we will consider "How STPA is being used in automotive cybersecurity" and we will introduce: -
STPA-Sec, what it is and why you should care.
How to implement TARA guidelines when using STPA-Sec.
Where threat modelling can be used and how to do so (i.e. STRIDE and beyond).
Designing-in effective safeguards begins at the concept phase, enables the definition and refinement of precise design recommendations, and continues throughout the product lifecycle, to operations and product retirement. Discover life beyond 21434…
또한 스폰서로 참여하여 TARA, STPA, FMEA, FTA의 안전 및 사이버보안을 분석을 지원하는 VisualPro 및 개발 SBOM 취약점 관리 및 CSMS 준수를 위한 Audit을 도와주는 ALM 도구 Teamer를 선보일 예정입니다.
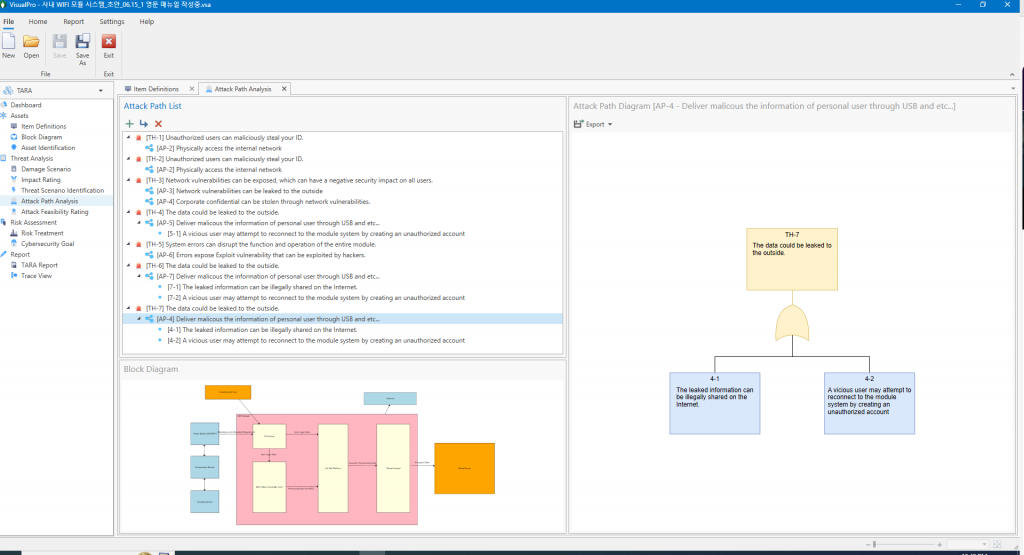
VisualPro TARA
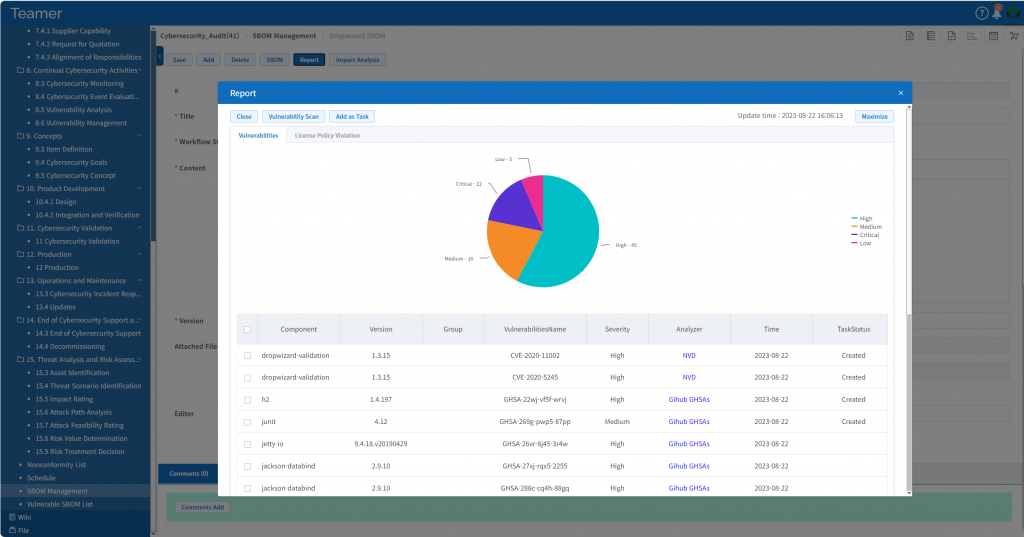
Teamer - SBOM Vulnerability Management
(주) 브이웨이는 2023년 11월 27일부터 30일까지 독일의 Leonardo Royal Hotel in Munich에서 열리는 Automotive Cyber Security Europe 행사에 참여합니다. 본 행사는 ISO/SAE 21434와 R155/R156의 대응을 위해 여러가지의 도전 과제들에 대한 의제를 나누고 해결점을 찾기 위해 유럽 및 전세계의 CyberSeucirty 전문가들이 모이는 컨퍼런스입니다.
특히 자사의 유럽 및 미국 영업 담당자인 Stephen Porter가 어떻게 STPA가 Cybersecurty에 활용될 수 있으며 ISO/SAE 21434에서 수행되는 TARA의 분석을 어떻게 뒷받침 할 수 있는지 발표가 준비되어 있습니다.
또한 스폰서로 참여하여 TARA, STPA, FMEA, FTA의 안전 및 사이버보안을 분석을 지원하는 VisualPro 및 개발 SBOM 취약점 관리 및 CSMS 준수를 위한 Audit을 도와주는 ALM 도구 Teamer를 선보일 예정입니다.
VisualPro TARA
Teamer - SBOM Vulnerability Management